How to detect non-CVE vulnerabilities that standard scanners miss
If your application security program only tracks known Common Vulnerabilities and Exposures (CVEs), you’re probably missing a large share of your real risk. Across the …
Cybersecurity best practices including how to guides, security awareness and other practical guidance for AppSec and ProdSec teams.
If your application security program only tracks known Common Vulnerabilities and Exposures (CVEs), you’re probably missing a large share of your real risk. Across the …
We’ve been listening to dozens of CISOs. In roundtables, peer forums, customer and prospect calls, on the record, off the record, at event floors and …
For years, development and security practitioners have treated dynamic application security testing as a critical final safety check before code goes live. However, the external …
Scaling application security and attack surface monitoring inside a single enterprise is a massive headache. In June 2026, the Department for Science, Innovation and Technology …
Attack Surface Monitoring has become a critical component of modern cybersecurity programs. As organizations scale their cloud environments, applications, APIs, and third-party services, so does …
Let’s be real. Shadow AI is already reshaping Shadow IT Security, whether organizations are ready or not. Chances are that your developers aren’t waiting for …
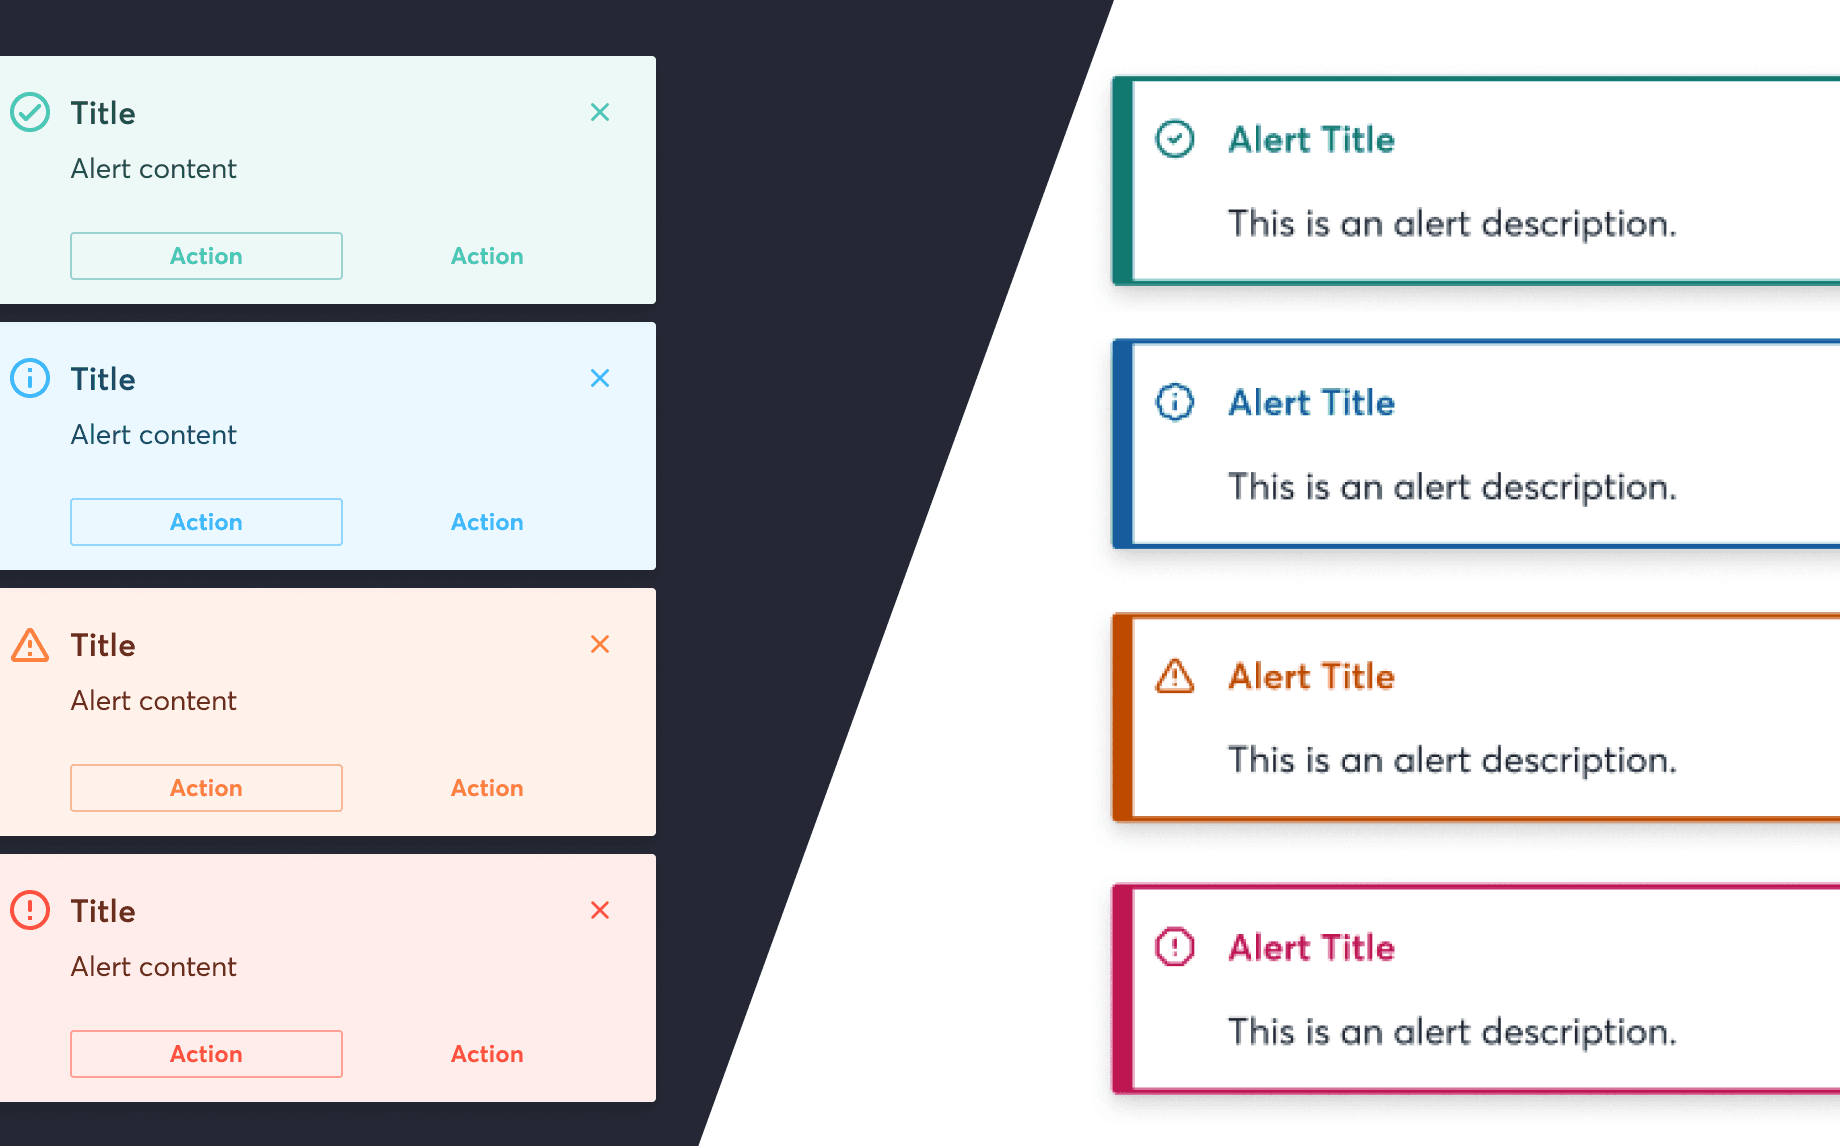
TL;DR: Building for everyone, faster. We’re moving from the why to the how. To scale accessibility without losing speed, we’ve overhauled our foundation: A New …
In cybersecurity, an inaccessible tool isn’t just a nuisance: it’s a vulnerability. With the European Accessibility Act tightening regulations across Sweden and the EU, “good …